
Hey Equalizers + Digital Guardians ⚖️🛡️,
This one deserves a deeper look because we’re talking about a government database containing some of the most sensitive information connected to Florida drivers.
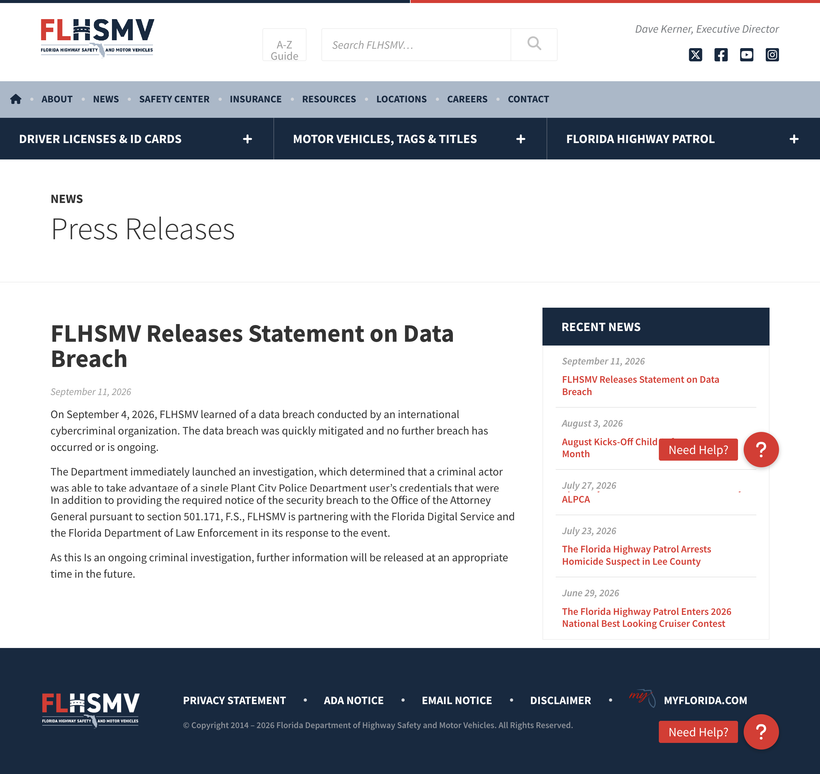
Florida has confirmed that an unauthorized actor gained access to the state’s DAVID system, which is used by authorized agencies to access driver and vehicle information.
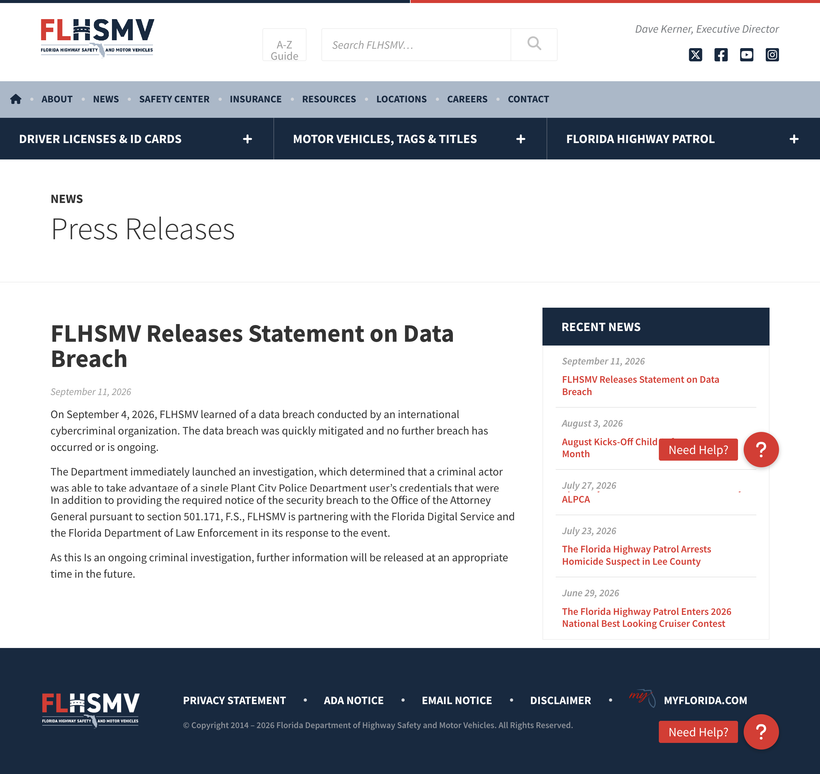
And according to FLHSMV, investigators traced the compromised access back to credentials belonging to one Plant City Police Department user that had been improperly stored on that employee’s personal electronic device.
That sentence alone should raise some serious cybersecurity questions.
The hacking/extortion group ShinyHunters claims it obtained more than 200,000 driver records and has claimed access to highly sensitive information.
But here is where keeping the receipts straight matters:
⚠️ Florida has confirmed the breach.
⚠️ Florida has confirmed the compromised credentials and personal-device issue.
⚠️ Florida has NOT publicly confirmed the hackers’ 200,000-record figure or every category of information they claim was taken.
Here’s some of the questions I have:
-
What information was actually downloaded or removed from the system?
-
How long did the unauthorized actor have access?
-
What security policies governed storing DAVID credentials on personal devices?
-
Were multifactor authentication or other access controls in place?
-
How many Floridians were actually affected?
-
Will affected drivers receive direct notification?
-
Has Florida identified whether those records are now being sold, shared or used elsewhere?
This is bigger than simply saying the breach has been “contained.” Containment stops continued access. It does not magically retrieve data that may have already been taken.
I’m including the receipts from the source and reporting below so you can read the receipts yourself.
And thank you to every paid Equalizer + Digital Guardian supporting independent investigative reporting, digital safety education and the work it takes to actually pull the documents instead of just reposting a headline.
Your support helps me keep doing exactly this. Like I always say, People Lie. Receipts Don’t.™ 🧾💜
📂 SOURCE RECEIPTS
🧾 Florida Highway Safety and Motor Vehicles statement on the DAVID security incident
Read the Press Release
🧾 Reporting detailing the ShinyHunters claims regarding the alleged number of records and information accessed
https://www.bleepingcomputer.com/news/security/shinyhunters-hackers-claim-breach-of-florida-david-dmv-database/
This story is still developing. I’ll update this post as more verified information becomes available.

0 Comments